iAmaze - EMS

Enterprise Mobility + Security

Endpoint Mgmt, Threat Defence & Identity Protection

68%

of data breaches involve an endpoint

74%

of orgs have no BYOD policy

3.4M

unmanaged devices in avg enterprise

21 Days

avg time to detect an insider breach

INR 17Cr

avg cost of a data breach in India

THE ENTERPRISE MOBILITY CHALLENGE

Why Endpoint Management, Threat Defence & Identity Are Inseparable

The modern workforce operates across corporate devices, personal phones, remote laptops, and hundreds of cloud applications. This creates three interconnected security risks: unmanaged endpoints that expose your organisation to breach, undetected endpoint threats that spread laterally, and unprotected identities that become the primary entry point for attackers. Addressing any one without the others leaves critical gaps.

Over 80% of security breaches involve compromised identities. 68% of data breaches involve an endpoint. Yet most organisations still manage devices, secure endpoints, and protect identities using separate, disconnected tools — creating blind spots that attackers exploit. Microsoft’s integrated EMS platform — Intune, Defender for Endpoint, and Entra ID — closes all three gaps through a single, unified, cloud-native security architecture.

SOLUTION 1 — MICROSOFT INTUNE

Unified Endpoint Management for Every Device, Every Platform

Microsoft Intune is a cloud-based unified endpoint management (UEM) platform and a core component of the Microsoft Enterprise Mobility + Security suite. It enables IT administrators to manage, secure, and configure every device across your organisation — from corporate Windows laptops to employee-owned Android phones — through a single, cloud-native admin console integrated natively with Defender and Entra ID

Intune supports both MDM (full device management for corporate assets) and MAM (app-level data protection for personal BYOD devices without managing the whole device). Combined with Defender for Endpoint, Intune enforces device health as a condition of access. Combined with Entra ID, it feeds device compliance signals into Conditional Access policies — creating a zero-trust architecture where only healthy, managed, compliant devices reach corporate resources.

Mobile Device Management (MDM)

Enrol and fully manage corporate-owned Windows 10/11, macOS, iOS, iPadOS, Android, and Linux devices. Enforce encryption, passcode policies, OS update requirements, and configuration profiles from a single cloud admin console.
Mobile Application Management (MAM)

Protect corporate data inside Microsoft 365 apps on personal BYOD devices without enrolling the whole device. App Protection Policies control copy/paste, save-as, and screen capture — protecting company data without touching personal content.
Compliance Policies & Security Baselines

Define what a healthy device looks like — antivirus enabled, OS patched, BitLocker on, no jailbreak — and automatically mark non-compliant devices. Integrate with Conditional Access to block non-compliant devices from email, SharePoint, and corporate apps.
Conditional Access Integration

Feed device compliance status from Intune into Entra ID Conditional Access policies — granting access to Microsoft 365, Azure, and corporate apps only from enrolled, compliant, healthy devices as part of a Zero Trust architecture.

App Deployment & Patch Management

Push mandatory or optional applications to all enrolled devices silently, without user interaction. Manage the full app lifecycle — deploy, update, configure, and retire apps — across Windows, macOS, iOS, and Android from one console.

Remote Wipe, Lock & Reset

Instantly perform a full wipe of a lost or stolen corporate device, or a selective wipe that removes only company data from a personal device. Remotely lock devices, reset PINs, and collect diagnostic logs without physical access.
Windows Autopilot & Zero-Touch Enrolment

New Windows devices are automatically enrolled and configured the moment an employee signs in — no IT department involvement required. Autopilot profiles pre-configure security settings, applications, and Defender policies before first use.
Endpoint Analytics & Reporting

Real-time dashboards show device compliance rates, OS version distribution, and policy deployment status across the entire device fleet. Endpoint Analytics identifies devices with startup issues, crashes, or app failures for proactive remediation.
SOLUTION 2 — MICROSOFT DEFENDER FOR ENDPOINT

AI-Powered Endpoint Detection, Response & Vulnerability Management

Microsoft Defender for Endpoint is an enterprise-grade endpoint security platform that goes far beyond traditional antivirus. It combines next-generation antivirus, endpoint detection and response (EDR), threat and vulnerability management, automated investigation and remediation, and advanced threat hunting — all in a single cloud-delivered platform natively integrated with Intune and Entra ID.

Named a Leader in the 2025 Gartner Magic Quadrant for Endpoint Protection Platforms for the sixth consecutive year. Defender for Endpoint processes over 84 trillion security signals daily, disrupts 35,000 cyberattack campaigns per month, and integrates with the full Microsoft Defender XDR suite for cross-domain threat correlation across email, identity, endpoint, and cloud. Plan 1 covers NGAV and attack surface reduction. Plan 2 adds full EDR, automated investigation, threat hunting, vulnerability management, and Microsoft Threat Experts.

Next-Generation Antivirus (NGAV)

Uses AI, machine learning, and behavioural analytics to detect and block malware, ransomware, fileless attacks, and zero-day exploits that signature-based antivirus cannot see. Cloud-delivered protection updates in real time without waiting for signature updates.
Endpoint Detection & Response (EDR)

Provides continuous monitoring of all endpoint activity with a searchable six-month device timeline. Security analysts can investigate suspicious processes, network connections, file modifications, and registry changes with forensic-grade visibility.
Threat & Vulnerability Management (TVM)

Continuously discovers and prioritises software vulnerabilities and misconfigurations across all managed endpoints using a risk-based scoring model. Provides direct remediation guidance and integrates with Intune to push patches and configuration fixes.
Attack Surface Reduction (ASR)

Minimises potential attack entry points by enforcing security controls that block exploit techniques — disabling macros in Office files from the internet, restricting credential theft from LSASS, blocking untrusted USB execution, and controlling network exposure.

Automated Investigation & Remediation (AIR)

When a threat alert is triggered, AIR automatically launches an investigation, determines the scope of the attack, identifies affected files and processes, and executes or recommends remediation actions — reducing alert investigation time from hours to minutes.

Advanced Threat Hunting

Security teams can proactively search for threats using KQL queries across up to 30 days of raw endpoint data. Custom detection rules generate alerts when specific patterns are detected, enabling proactive threat discovery before alerts are triggered.
Microsoft Defender XDR Integration

Defender for Endpoint is a native component of Microsoft Defender XDR, correlating endpoint signals with email, identity, and cloud security data in a unified incident view — enabling faster, more complete threat investigation and response across domains.
Mobile Threat Defence (iOS & Android)

Extends endpoint protection to mobile devices — detecting and blocking phishing attempts, malicious apps, network attacks, and device vulnerability exploitation on iOS and Android, fully integrated with Intune MAM and device compliance policies.
BUSINESS BENEFITS

Organisations That Should Deploy Microsoft EMS Now

Organisations with 50+ employees using a mix of corporate devices, personal phones, and remote laptops that need unified management and compliance enforcement

Businesses adopting Microsoft 365 that want to extend security beyond email to full device management, endpoint protection, and identity governance

Companies implementing a Zero Trust security model that requires device health, identity verification, and threat posture checks before every access request

IT teams that currently manage devices, secure endpoints, and protect identities with separate disconnected tools and want a unified Microsoft-native platform

Organisations in regulated industries — BFSI, healthcare, legal, government — with compliance obligations requiring device compliance evidence, audit logs, and access controls

Businesses that have experienced identity-based attacks, phishing compromises, or endpoint breaches and need a proven, enterprise-grade defence platform

UNIFIED EMS ARCHITECTURE

How Intune, Defender & Entra ID Work as One Integrated Platform

Microsoft’s EMS platform is not three separate products — it is one unified security architecture. Entra ID provides the identity control plane, Intune provides the device management plane, and Defender provides the threat protection plane. Every signal from each platform enriches the others, creating a feedback loop that improves security posture across your entire organisation.

Identity as the First Gate — Entra ID

Every access attempt first passes through Entra ID. The identity, device compliance status (from Intune), and threat signal (from Defender) are evaluated together by Conditional Access before any resource is granted.
Device as the Second Gate — Intune

Only devices enrolled in Intune and marked compliant can satisfy device-based Conditional Access conditions. Non-compliant or unmanaged devices are blocked at the identity layer before they can reach any corporate application.
Threat as the Third Gate — Defender

Defender feeds real-time device health and threat signals into Intune compliance. A device under active attack or with a high threat risk score is automatically marked non-compliant, blocking its access until the threat is remediated.
Zero Trust Access Model

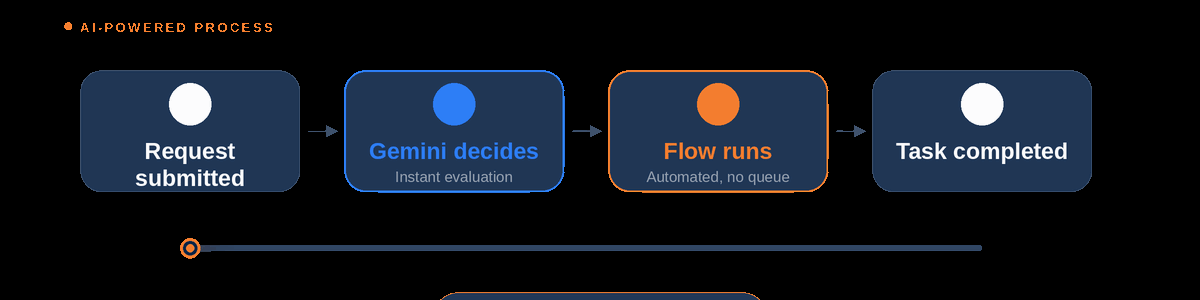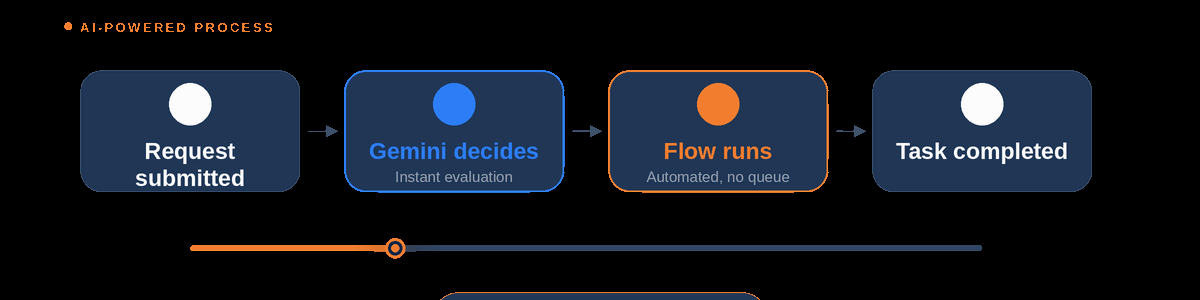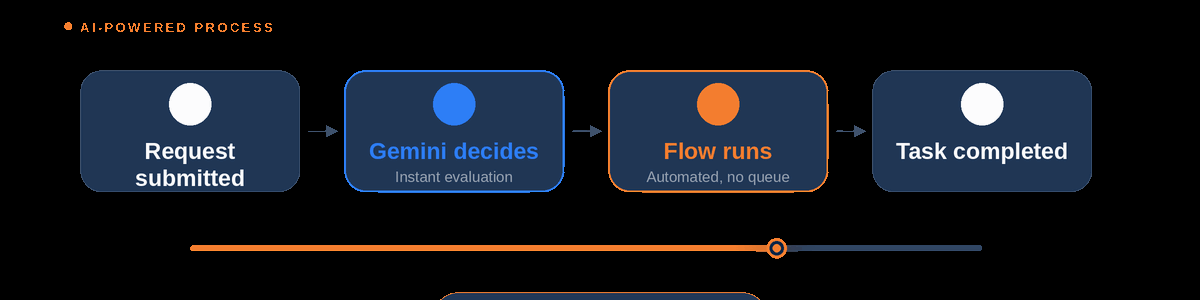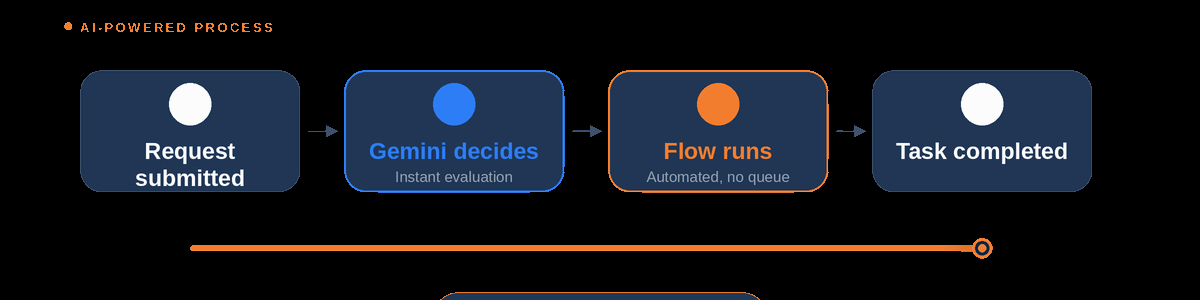
The integration of Intune + Defender + Entra ID creates a true Zero Trust architecture: every access request is verified by identity (Entra), device health (Intune), and threat posture (Defender) before access is granted — regardless of network location
Automated Response Across Layers

When Defender detects a compromised device, it signals Intune to mark it non-compliant. Intune feeds this to Entra ID Conditional Access, which automatically restricts the user’s access. This cross-layer response happens in minutes without human intervention.
Single Admin Console — Microsoft Defender XDR Portal

Security administrators manage all three products from the unified Microsoft Defender XDR portal and the Intune admin centre — with a single pane of glass for device compliance, threat incidents, identity risks, and policy management.
WHY iAMAZE

Your Dedicated Microsoft EMS Implementation Partner

iAmaze manages the full Microsoft EMS lifecycle — from initial security assessment and architecture design through Intune device enrolment, Defender deployment, Entra ID configuration, Conditional Access policy design, user training, and ongoing managed security operations.

EMS Assessment

We audit your current device fleet, identity posture, endpoint threat exposure, and access control gaps. We map the right combination of Intune, Defender, and Entra ID licences for your organisation size and security requirements.

Microsoft Intune Deployment

We enrol all corporate and BYOD devices via Autopilot, bulk enrolment, or MDM profiles. We configure compliance baselines, app protection policies, app deployments, and integration with Defender for device health signals.

Microsoft Defender Deployment

We deploy Defender for Endpoint across all managed devices via Intune policy. We configure NGAV settings, EDR onboarding, ASR rules, vulnerability management baselines, and automated investigation policies.

Entra ID Configuration

We design and implement Conditional Access policies, MFA enforcement, SSPR, Identity Protection risk policies, PIM for admin roles, and hybrid identity sync from on-premises Active Directory.

Zero Trust Architecture Design

We create an integrated Conditional Access framework that combines Intune compliance, Defender threat signals, and Entra ID identity risk into a unified Zero Trust access model tailored to your organisation.

24/7 Managed SOC

Ongoing monitoring of Intune compliance dashboards, Defender incident queues, and Entra ID risky sign-in alerts. Proactive alert triage, incident response, policy optimisation, and quarterly EMS health reviews.

HOW WE WORK

Our Four-Step EMS Engagement Model

From your first call to a fully deployed, integrated EMS platform — a structured, expert-led approach with zero disruption to your users or existing infrastructure.

EMS Assessment

Audit your device fleet, identity posture, and threat exposure. Map gaps across device management, endpoint security, and identity access controls.
Solution Design

Right-size Intune, Defender, and Entra ID licences. Design Conditional Access policies, compliance baselines, and Autopilot enrolment strategy.
Deployment & Integration

Enrol all devices into Intune, deploy Defender via Intune policy, configure Entra ID SSO, MFA, Conditional Access, and Identity Protection rules.
Training & Managed SOC

Admin training on all three portals. 24/7 monitoring of Intune compliance alerts, Defender incidents, and Entra ID risky sign-ins. Quarterly EMS reviews.