iAmaze - AI Automation Specilist

Data Security

DLP, Insider Threat & Data Discovery

60%

Data breaches caused by insider threats

$4.9M

Average cost of a data breach 2024

277

Days avg time to identify a breach

83%

Orgs had more than one breach in 2024

INR 17Cr

Avg breach cost in India (IBM 2024)

THE DATA SECURITY CHALLENGE

Why Sensitive Data Is Your Organisation’s Most Critical Risk

Data is the most valuable asset in any organisation — and the most targeted. Intellectual property, customer records, financial data, and regulated information face constant risk from insider threats, accidental leakage, malicious exfiltration, and compliance failures. A single data breach now costs an average of $4.9 million and takes 277 days to detect and contain — with insider-related incidents among the costliest and most difficult to identify.

60% of data breaches involve an insider — whether malicious, negligent, or compromised. Traditional perimeter security cannot protect data that moves via email, USB, cloud uploads, screenshots, or employee devices. Organisations need a dedicated Data Loss Prevention (DLP) strategy that combines content-aware monitoring, user behaviour analytics, data discovery, and insider threat management — applied at the endpoint, email, and network layers simultaneously.

SOLUTION 1 — INDEFEND ADVANCED BY DATARESOLVE

DLP + Insider Threat Management + Employee Monitoring — Made in India

inDefend Advanced by DataResolve is India’s leading endpoint DLP and insider threat management platform, trusted by 200+ customers across 20 industries and 1,00,000+ secured endpoints. Recognised by DSCI/NASSCOM, Silicon India, and featured on CNBC18 and ET Now, inDefend provides complete visibility and control over how sensitive data moves through your organisation — across endpoints, email, cloud, printers, and mobile devices.

inDefend is the only Indian-built DLP solution that combines endpoint DLP, insider threat detection, and employee productivity monitoring in a single unified platform. It operates as a lightweight stealth agent that monitors all user activity in real time — USB transfers, email attachments, file uploads, print jobs, and screenshots — without impacting system performance. Particularly valuable for Indian enterprises facing notice period data theft, employee misconduct investigations, and IP protection requirements.

Data Leak Prevention (DLP)

All Channels Blocks and logs data leakage across every exfiltration channel: USB drives, external storage, email attachments (M365, Google Workspace, Zimbra), web uploads, FTP, cloud storage, chat applications (WhatsApp, Teams, Telegram), and print jobs.
Insider Threat Detection & Prevention

Real-time behavioural analysis continuously monitors user activity and flags anomalies — unauthorised file access, bulk data movement, suspicious application usage, or off-hours activity. Proactive alerts notify security teams before a breach occurs.
Device & USB Control

Whitelist approved USB devices and block all others by vendor ID and serial number. Enforce encryption on removable media. Control cameras, Bluetooth, printers, and peripheral devices at the policy level across all managed Windows endpoints
Content-Aware Monitoring

Detects sensitive data — PAN numbers, Aadhaar details, financial records, intellectual property, and custom keywords — in files, emails, and chat messages whether the data is in motion, in use, or at rest on the endpoint.
Employee Productivity Analytics

Generates detailed productivity reports showing active work time, idle time, application usage, and website visits per employee. Identifies low-productivity patterns, moonlighting risks, and employees showing resignation intent — critical for Indian enterprises.

Stealth Agent & Shadow Logging

The inDefend agent operates invisibly on Windows endpoints with minimal CPU and memory usage. All user activities are logged to a central server with a tamper-proof audit trail. Email and SMS alerts for real-time incident notifications to administrators.

Screenshot & Print Control

Optionally capture covert screenshots of employee activity for security investigations. Block unauthorised screen capture tools. Monitor and control all print jobs including document content, page counts, and printer destinations.
Roaming & Remote Worker Coverage

Protects in-office desktops and roaming laptops regardless of VPN connectivity. Policies apply offline and sync incident logs when the device reconnects. Specifically designed for monitoring employees on notice period.
SOLUTION 2 — ZECURION NEXT GENERATION DLP

10+ Detection Technologies · UBA · DCAP · Deploy in 2 Business Days

Zecurion Next Generation DLP is a technologically advanced enterprise data protection platform that combines more than 10 detection technologies, User Behaviour Analytics (UBA), and its Data-Centric Audit and Protection (DCAP) module into a single, easy-to-deploy solution. With 5-star ratings on Gartner Peer Insights and deployment achievable within 2 business days, Zecurion is built for organisations that need powerful protection without operational complexity.

Zecurion’s unique Screen Photo Detector uses dual neural networks to detect smartphone camera presence at a workstation within 0.06 seconds — instantly darkening the screen or locking the device before a photo can be taken. This revolutionary capability is combined with dynamic watermarking that overlays user names, timestamps, and device IDs on sensitive windows (CRM, Office, EHR systems) to deter and forensically track data theft through physical means — a growing exfiltration vector that traditional DLP cannot address.

10+ Detection Technologies

Accuracy Zecurion combines digital document fingerprints, probabilistic analysis, regular expressions, attribute filtering, data templates, linguistic analysis, OCR (optical character recognition), signature analysis, transliteration analysis, and AI-based image recognition — minimising false positives while maximising detection accuracy.
User Behaviour Analytics (UBA)

10+ Indicators Calculates more than 10 behavioural risk indicators per user including emotional profiling, activity deviations, and relationship mapping across 150 communication channels. The interactive user connection graph reveals hidden relationships and suspicious communication patterns within the organisation.
Screen Photo Detector — 0.06 Second Response

Detects smartphone cameras positioned near workstation screens using dual neural networks.In 0.06 seconds the system darkens the screen, locks the device, or triggers an alert. Dynamic watermarking overlays user identification on sensitive windows as both a deterrent and forensic tool for investigations.
DCAP — Data-Centric Audit & Protection

Automatically discovers, classifies, and tracks all sensitive data across endpoints, databases, SharePoint, and cloud storage using 10+ proprietary technologies. AI-based image templates and OCR identify structured documents and scanned data. Violations trigger automated responses like access revocation or file deletion.
100+ Channel Monitoring

Monitors and controls data movement across more than 100 communication services including all email platforms, WhatsApp, Telegram, Skype, Microsoft Teams, cloud storage, FTP, USB, and printers. Complete archive of all events with file and attachment copies for forensic investigation.

Incident Investigation & Forensics

A full archive of all events, file copies, and employee communications supports fast, easy forensic investigations. Pre-built with 50+ report templates and interactive dashboards. 75% faster investigation time compared to manual review processes. Fully compliant with GDPR, PCI, HIPAA, SOX, and ISO requirements.

Policy-Based Controls — Role & Risk

Restrict data access based on user roles and privileges. Block data transmission via email, cloud services, or removable media based on content classification and user risk scores. Automated policy responses based on data sensitivity level and individual user risk profile.
2-Day Deployment — Out-of-Box Templates

Uniquely easy to deploy with detailed step-by-step instructions. 20+ policy templates ready for immediate use. No extra charge for deployment and configuration support. Dedicated account manager with 24/7 technical support via phone, email, and messenger. Software works indefinitely even after support subscription expires.

SOLUTION 3 — TREND MICRO — DATA SECURITY & DLP

Integrated DLP Across Endpoint, Email, Cloud & Network — via Trend Vision One™

Trend Vision One™ delivers modern data security that goes beyond legacy DLP — combining data discovery, classification, policy enforcement, user behaviour analytics, and XDR correlation in a single unified platform. With a single lightweight agent that covers endpoint security and integrated DLP simultaneously, Trend Micro reduces deployment complexity while delivering enterprise-grade data protection across every channel where data moves.

Trend Micro’s integrated DLP recognises and processes over 300 file types — including email clients, Office applications, programming files, graphics, engineering files, and compressed archives. Pre-built compliance templates for GDPR, HIPAA, PCI DSS, and other regulations enable rapid deployment. The platform integrates with Microsoft Purview Information Protection sensitivity labels, enabling organisations already using Microsoft’s data classification framework to extend it seamlessly into Trend’s unified security platform.

Data in Motion — Network & Communication Control

Provides visibility and control over data transmitted via email, webmail, instant messaging applications, FTP, HTTP/HTTPS, and SMTP. Policy-based responses include monitor, block, quarantine, alert, modify, or delete — applied automatically based on content detection and classification rules.

Data in Use — Endpoint Channel Control

Controls data movement on endpoints via USB ports, CD/DVD writers, removable disks, COM and LPT ports, PCMCIA cards, infrared and imaging devices, and modems. Also monitors copy-paste operations and print screen events to prevent visual exfiltration at the endpoint

Data at Rest — Discovery & Scanning

Scans endpoints, file servers, mail stores, and SharePoint repositories to discover where regulated or sensitive data resides. Supports over 300 file types. Automated discovery reports highlight compliance data locations, enabling targeted protection and access control before incidents occur.

Data Classification & Microsoft Purview Integration

Built-in data templates and customisable classification policies identify sensitive data across all channels. Integrates with Microsoft Purview Information Protection sensitivity labels — allowing organisations to use their existing Microsoft data classification framework within Trend Vision One’s DLP engine.

Integrated DLP + Endpoint Security — Single Agent

Trend Micro’s integrated DLP shares a single lightweight agent with endpoint security, device control, and XDR — reducing resource demand, performance impact, and deployment complexity. IT teams manage all security and DLP policies from one console without separate product management overhead.

200+ Compliance Templates

Pre-built templates for GDPR, HIPAA, PCI DSS, ISO 27001, SOX, and regional data protection regulations enable rapid compliance enablement. Templates define sensitive data patterns, channel controls, and automated response actions — reducing policy setup time from weeks to hours.

XDR Correlation — Data + Threat Context

Trend Vision One correlates DLP incidents with endpoint threat signals, email security detections, and identity risk data through native XDR. Security teams can see whether a data exfiltration attempt is linked to a compromised account, active malware, or a malicious insider — enabling faster, more targeted response.

Device Control — Granular Rules

Offers granular device control with the ability to create specific rules based on vendor ID and serial number of specific devices. IT administrators can allow trusted USB devices while blocking all others, creating a flexible policy framework that supports legitimate business use without compromising security.

DATA SECURITY ARCHITECTURE

Discover, Classify, Prevent & Monitor Across Every Data Channel

Effective data security requires protecting data at every stage of its lifecycle — at rest, in use, and in motion. iAmaze designs a layered data security architecture that combines discovery and classification, prevention across all channels, user behaviour monitoring, and continuous managed oversight.

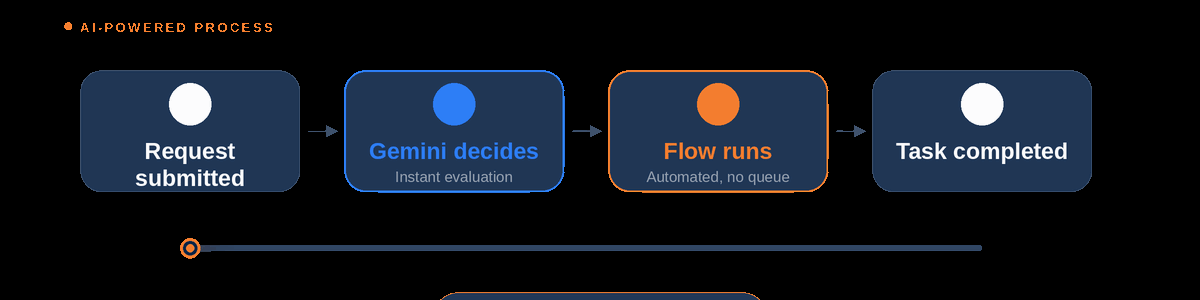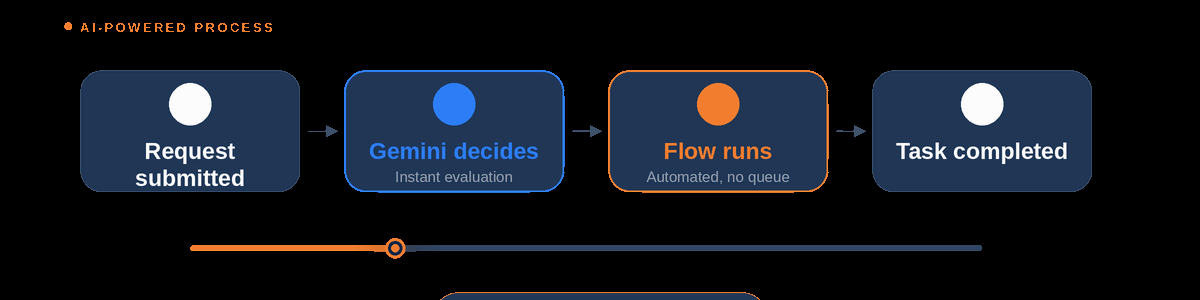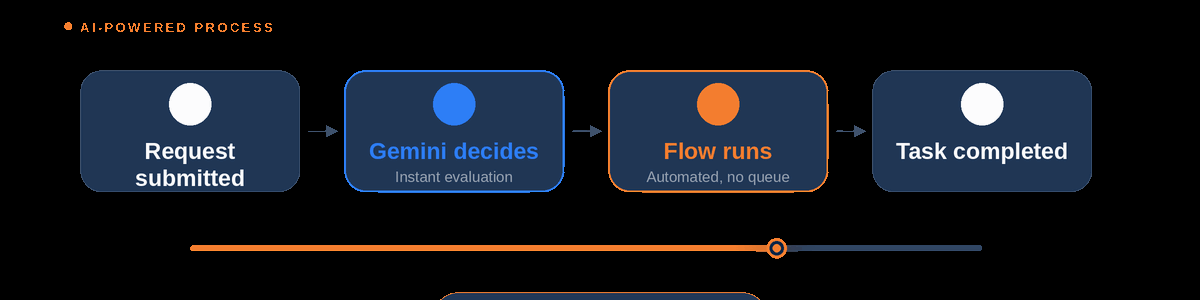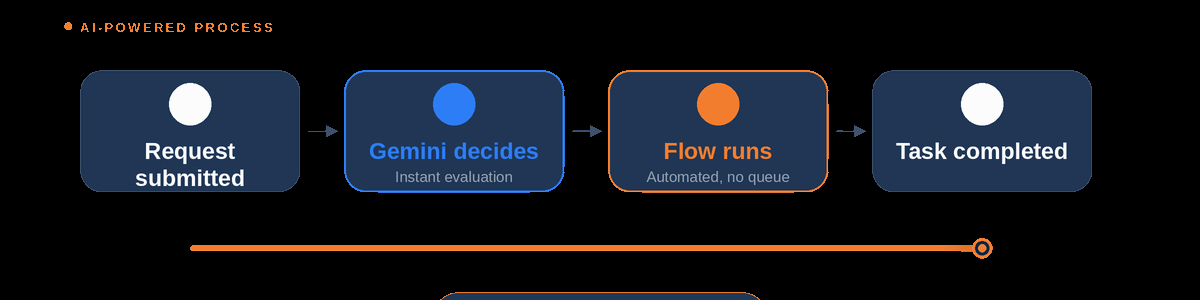
Input

Email, Document forms or trigger arrives

AI Leads

Google AI Studio undertand & Extract intent

AI Decids

Gemini classifiels. the routes and chooses best actions

Flow Runs

Power automate and executes the correct workflow

Apps Updated

CRM, ERP , Email stack ,share point all updated

Outcome

Task compete human notified audit trail saved

Discovery & Classification Layer

Before you can protect data, you must know where it lives. Zecurion DCAP and Trend Micro’s data-at-rest scanning discover and classify sensitive data across endpoints, email stores, SharePoint, databases, and cloud storage — creating a complete data landscape map.

Prevention Layer — All Three Products

inDefend, Zecurion, and Trend Micro DLP all apply policy-based controls at the point of data movement — blocking unauthorised transfers via email, USB, cloud uploads, print, messaging, and web. Together they cover every exfiltration channel an insider could use.

Monitoring & UBA Layer

User Behaviour Analytics from all three platforms continuously profiles normal activity patterns and flags deviations — unusual file access volumes, off-hours data movement, bulk downloads, or communication with competitors — providing early warning of insider threats before exfiltration occurs.

Physical Exfiltration Prevention

Zecurion’s unique Screen Photo Detector and inDefend’s print/screenshot controls address the physical exfiltration channel — protecting against employees photographing screens or printing sensitive documents to remove from the office.

iAmaze Managed SOC

iAmaze provides 24/7 monitoring of DLP incidents and UBA alerts across all deployed platforms. Security analysts triage alerts, investigate incidents, tune policies to reduce false positives, and provide daily threat intelligence reports to your security leadership.

Compliance & Audit Readiness

All three platforms generate compliance-ready audit logs, incident reports, and policy enforcement evidence. Combined with iAmaze’s quarterly compliance reviews, your organisation can demonstrate data protection controls to auditors, regulators, and cyber insurance providers.
BUSINESS BENEFITS

Organisations That Need Data Security Solutions Now

Organisations that handle sensitive customer data, financial records, intellectual property, or regulated information and lack dedicated DLP controls

Indian businesses facing data theft during employee exits, notice periods, or layoffs where bulk data exfiltration to USB or personal email is a known risk

Companies in regulated industries — BFSI, healthcare, legal, pharma, IT/ITES — with compliance obligations under PDPB, GDPR, PCI DSS, HIPAA, or ISO 27001

Organisations that have experienced a data breach, IP theft, or compliance violation and need to demonstrate remediation controls to regulators or auditors

Businesses managing remote or hybrid workforces that need DLP coverage across roaming laptops, personal devices, and cloud applications

IT and security teams seeking to move beyond basic endpoint security to a comprehensive data-centric security strategy with audit trail and forensic capabilities

WHY iAMAZE

Your Dedicated Data Security Implementation Partner

iAmaze provides end-to-end data security services across all three platforms — from initial data security assessment and vendor-neutral recommendation through deployment, data classification policy design, compliance template configuration, user training, and ongoing managed security operations.

Data Security Assessment

We map all sensitive data flows in your organisation, identify leakage channels, quantify insider threat risk, assess existing DLP coverage gaps, and produce a prioritised remediation roadmap.

Product Selection

Vendor-neutral guidance to match the right solution: inDefend for Indian enterprise endpoint DLP + insider threat + productivity, Zecurion for advanced UBA + data discovery + screen protection, or Trend Micro for integrated DLP + XDR on a single agent.

Deployment & Integration

We deploy the chosen solution across all endpoint types, configure DLP channel policies, data classification templates, USB whitelists, UBA baselines, and compliance rules — typically live within 48–72 hours.

Policy & Data Classification

We build content-aware DLP policies tailored to your organisation’s data types: financial records, customer PII, Aadhaar/PAN data, intellectual property, source code, and regulated information categories.

User Awareness Training

We deliver end-user awareness sessions on data handling policies, acceptable use guidelines, and the consequences of policy violations — turning employees from a data security risk into a human firewall.

24/7 Managed SOC

Ongoing monitoring of DLP incidents and UBA alerts, proactive alert triage, policy tuning to reduce false positives, incident response support, and quarterly data security posture reviews with your security leadership.

HOW WE WORK

Our Four-Step Data Security Engagement

From your first call to fully deployed data protection — a structured, expert-led approach that minimises disruption while maximising coverage.

Data Security Assessment

Map all sensitive data flows, identify leakage channels, quantify insider risk exposure, and assess current DLP coverage gaps across your organisation.
Solution Design

Recommend the right product or combination: inDefend for endpoint DLP + insider threat, Zecurion for advanced UBA + data discovery, or Trend Micro for integrated DLP + XDR.
Deployment & Policy Setup

Deploy chosen solution agents, configure DLP channel policies, data classification rules, UBA baselines, and compliance templates. Typically live within 48–72 hours.
Training & Managed SOC

Admin training, end-user awareness sessions, 24/7 monitoring of DLP incidents and UBA alerts, incident response, policy optimisation, and quarterly data security reviews.