iAmaze - Endpoint Security

Endpoint Security

Advanced Protection for Every Device

1/39s

Ransomware attack occurs globally

71%

Attacks exploit stolen credentials

68%

Breaches involve an endpoint device

300K

New malware samples detected daily

$4.9M

Avg cost of an enterprise data breach

THE ENDPOINT THREAT LANDSCAPE

Why Every Device in Your Organisation Is a Target

Endpoints — laptops, desktops, servers, and mobile devices — are the primary target of modern cyberattacks. A ransomware attack occurs somewhere in the world every 39 seconds. Over 300,000 new malware samples are detected daily. Fileless attacks, zero-day exploits, and AI-generated phishing are outpacing traditional antivirus defences, demanding a new generation of intelligent, behavioural endpoint protection.

Traditional antivirus alone is no longer sufficient. Modern endpoint threats are polymorphic, fileless, and specifically engineered to evade signature-based detection. Organisations need multi-layered endpoint security that combines next-generation antivirus (NGAV), endpoint detection and response (EDR), threat intelligence, and automated remediation — deployed and managed by experts who monitor threats around the clock.

SOLUTION 1 — TREND VISION ONE™

Endpoint Security with Native XDR — Gartner EPP Leader Since 2002

Trend Vision One™ Endpoint Security is an AI-powered, XDR-integrated endpoint protection platform that defends every stage of the attack lifecycle — from prevention through detection, investigation, and response. It delivers the industry’s broadest endpoint coverage including workstations, servers, cloud workloads, containers, IoT devices, and legacy systems, all managed from a single unified console.

Named a Leader in the Gartner Magic Quadrant for Endpoint Protection Platforms continuously since 2002 — over two decades of recognition. Trend Vision One consolidates and correlates data from the industry’s largest native telemetry sensor network, enabling more accurate detection and 80% faster response times. The platform’s Proactive AI Security (Cybertron) predicts and blocks attacks before they execute, going beyond reactive detection.

XGen™ Multi-Layer Protection

Trend’s cross-generational security combines signature-based detection, machine learning, behavioural analysis, web reputation filtering, and exploit prevention in a single lightweight agent — blocking known and unknown threats across every attack vector.
Native EDR + XDR Integration

Integrated EDR capabilities provide prioritised, actionable alerts and comprehensive incident views. Extended to XDR, Trend Vision One correlates endpoint signals with email, cloud, network, and identity data for an attack-centric view across your entire organisation.
Attack Surface Risk Management (CREM)

Continuously discovers and assesses the risk exposure of every endpoint, user, and application in your environment. Provides a risk score and prioritised remediation steps — enabling proactive security before threats are exploited.
Proactive AI Security — Trend Cybertron

The industry’s first proactive AI platform for cybersecurity. Cybertron analyses threat patterns and predicts attacker behaviour before incidents occur, automatically adjusting defence postures and recommending preventive actions in real time.

Workload & Server Security

Provides comprehensive protection for physical servers, virtual machines, cloud workloads, containers, and Kubernetes clusters. Automated discovery of workloads across AWS, Azure, and Google Cloud enables consistent security policy enforcement everywhere.

Managed XDR — 24/7 Expert Analysts

Optional Managed XDR service augments your internal security team with Trend’s expert analysts providing round-the-clock threat monitoring, hunting, and guided investigation — dramatically reducing mean time to detect and respond.
Ransomware & Fileless Attack Prevention

Behavioural monitoring detects ransomware encryption patterns and terminates malicious processes before data is encrypted. Fileless attack prevention catches script-based, memory-resident, and living-off-the-land techniques that leave no files on disk.
Mobile & IoT Endpoint Protection

Extends endpoint security to iOS, Android, and IoT devices through Trend Vision One’s unified platform. Mobile Threat Defence detects phishing, malicious apps, and network attacks on mobile devices with full EDR visibility
SOLUTION 2 — WATCHGUARD EPDR

Zero-Trust Endpoint Protection, Detection & Response

WatchGuard EPDR (Endpoint Protection, Detection and Response) is a uniquely prevention-first endpoint security solution built on the Zero-Trust Application Service — a managed service that classifies 100% of all applications before allowing them to execute. Named a Leader and Outperformer in the 2025 GigaOm Radar for EDR, WatchGuard stops unknown threats before execution rather than relying on detection after the fact.

WatchGuard’s Zero-Trust Application Service automatically classifies 99.98% of all running processes using AI, with the remaining 0.02% manually classified by cybersecurity experts — ensuring 100% classification with zero false positives. Unknown applications are blocked by default, not allowed. This prevention-first model results in far fewer security incidents, dramatically lower alert volumes, and significantly reduced incident response burden compared to detection-based solutions.

Zero-Trust Application Service

The cornerstone of WatchGuard EPDR. Every application, process, and executable on every endpoint is classified as trusted or malicious before it can run. Untrusted processes are blocked automatically — zero unknown applications execute. This eliminates the risk of zero-day malware, ransomware, and fileless attacks that rely on new or unknown executables.
Managed Threat Hunting Service

WatchGuard’s expert cybersecurity analysts proactively hunt for advanced threats and indicators of attack (IoAs) based on the MITRE ATT&CK framework. They investigate anomalous usage of trusted applications — detecting hackers living off the land — and deliver actionable intelligence directly to customers.
Self-Learning AI — EDR Capabilities

Self-learning AI automatically detects indicators of attack (IoAs), malicious scripts, fileless attacks, in-memory exploits, and ransomware. Machine learning analysis of installers, PDFs, and Office files at pre-execution stage blocks hidden threats before any code runs.
Ransomware Prevention & Containment

Stops ransomware before it spreads across endpoints and the network. WatchGuard’s prevention-first architecture means ransomware is blocked at the execution stage — not detected after files are already encrypted, as is the case with purely reactive solutions.

ThreatSync — XDR Correlation

Connects detections from the Zero-Trust Application Service and Threat Hunting Service across the entire WatchGuard ecosystem. ThreatSync correlates Indicators of Compromise (IoCs) from endpoint, network, Wi-Fi, and identity products into unified incident views with coordinated response actions.

URL Filtering, Device Control & Firewall

Full EPP capabilities including URL and content filtering to block web-based threats, USB device control to prevent data exfiltration via removable media, and a managed firewall with application-aware policy enforcement — reducing the attack surface significantly.
Lightweight Agent — MSP-Ready Platform

WatchGuard EPDR uses a lightweight agent with minimal impact on endpoint performance. The cloud-based management console is purpose-built for MSPs, supporting multi-tenant management, automated policy deployment, and detailed reporting across all customer environments.
Advanced EPDR — GenAI Telemetry Assistant

WatchGuard Advanced EPDR adds a GenAI Telemetry Assistant for natural-language investigation queries, proactive security posture assessments, supply chain risk mitigation via XDR integration, and AI-driven signal correlation for faster incident investigations.

SOLUTION 3 — KASPERSKY NEXT

#1 in 90% of 2025 Independent Tests — Six-Layer Endpoint Protection

Kaspersky Next is a comprehensive endpoint security platform trusted by nearly 200,000 corporate clients globally and protecting over one billion devices to date. Built on Kaspersky’s unparalleled threat intelligence from the Global Research and Analysis Team (GReAT) and a unique six-layer detection engine, Kaspersky Next delivers consistently top-rated protection in independent tests — earning the AV-TEST Best Protection award and SE Labs Winner Enterprise Endpoint 2025 recognition.

In 2025, Kaspersky business solutions were evaluated in 100 independent tests and reviews — securing first place in 90% of assessments and placing in the top three in 94%. The six-layer detection engine analyses 100,000+ features per file using machine learning, combining signature detection, heuristics, cloud sandbox, behavioural blocking, and cloud reputation to stop ransomware, worms, fileless attacks, and reverse shells before execution or spread.

Six-Layer Detection Engine

Kaspersky’s unique multi-layer approach combines: (1) signature detection for known malware, (2) heuristic analysis for variants, (3) machine learning scanning 100,000+ features, (4) cloud sandbox emulation, (5) behavioural blocking for fileless attacks, and (6) cloud reputation scoring for zero-days — all in a single lightweight agent.

Next-Gen EDR — Root Cause Analysis

Kaspersky Next EDR provides comprehensive visibility across all endpoint activity with clear visual attack maps, MITRE ATT&CK framework mapping, and root cause analysis showing the complete attack chain. Security teams can investigate, contain, and remediate threats from a single incident card view.

Automated Ransomware Rollback

Kaspersky’s unique Remediation Engine automatically rolls back ransomware-caused file changes, restoring encrypted files to their pre-attack state. This critical capability minimises business disruption even in the rare case ransomware executes before being detected.

Exploit Prevention

Prevents exploitation of memory vulnerabilities and zero-day exploits in legitimate applications. Behavioural analysis detects and blocks privilege escalation, injection attacks, and living-off-the-land techniques targeting Microsoft Office, browsers, and OS components.

Vulnerability Assessment & Patch Management

Continuous scanning of all endpoints identifies unpatched software vulnerabilities, misconfigurations, and security weaknesses. Cloud discovery identifies shadow IT and unsanctioned applications. Integrates with patch management workflows to close vulnerability windows rapidly.

File, Mail, Web & Network Protection

Stops attacks before or at earliest stages of execution. File Protection scans all file activity in real time. Mail Protection checks all incoming and outgoing emails. Web Protection blocks malicious URLs. Network Protection detects port scans, network attacks, and ARP spoofing.

Kaspersky GReAT — Threat Intelligence

The Global Research and Analysis Team (GReAT) is one of the world’s most respected threat intelligence teams. In 2025, GReAT uncovered a Chrome zero-day using Kaspersky Next EDR Expert. Threat intelligence feeds are continuously updated and delivered to all endpoints in real time.

Transparent Source Code & Trust Centres

Kaspersky operates global Transparency Centres where independent reviewers can inspect product source code, software updates, and threat detection rules. This level of transparency is unique in the endpoint security industry and addresses compliance and sovereignty requirements.

LAYERED DEFENCE ARCHITECTURE

Prevention, Detection & Response Across the Full Attack Lifecycle

Effective endpoint security is not a single product — it is a layered strategy. Whether you deploy one of these solutions or a complementary combination, iAmaze designs your endpoint security architecture to cover every phase of the attack lifecycle: prevention at the perimeter, detection in real time, response and containment, and recovery with full audit trail.

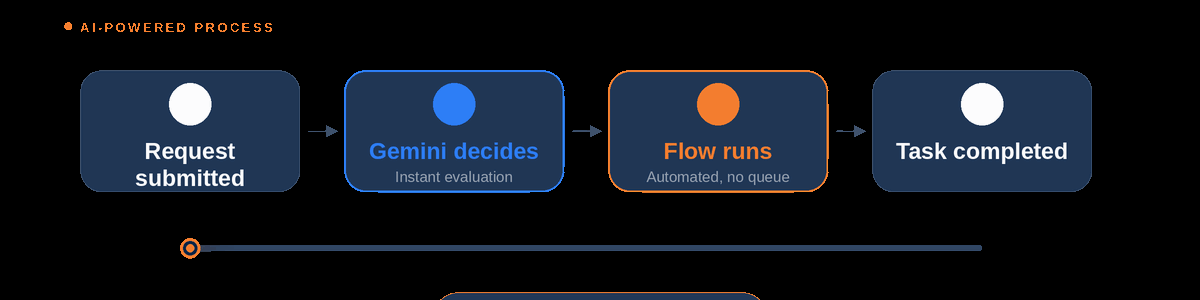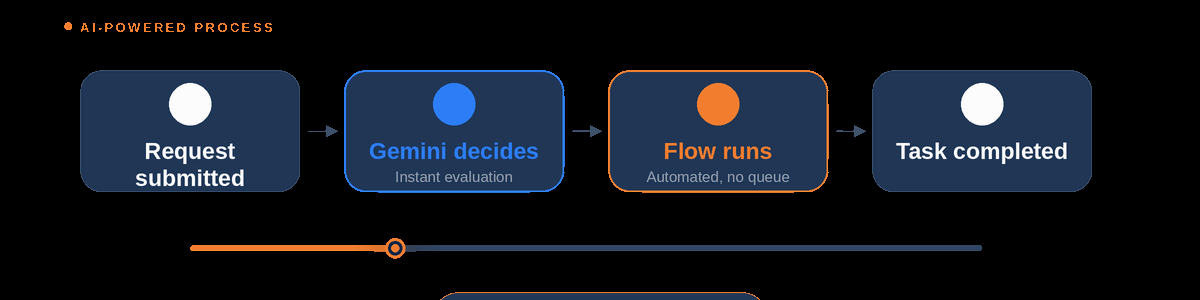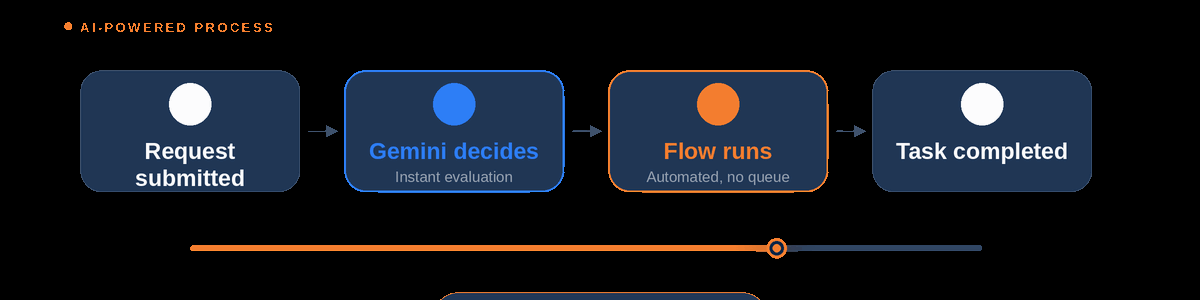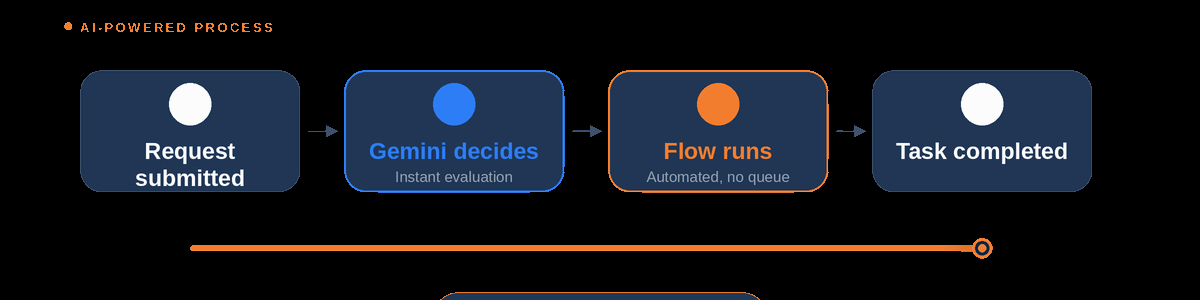
Input

Email, Document forms or trigger arrives

AI Leads

Google AI Studio undertand & Extract intent

AI Decids

Gemini classifiels. the routes and chooses best actions

Flow Runs

Power automate and executes the correct workflow

Apps Updated

CRM, ERP , Email stack ,share point all updated

Outcome

Task compete human notified audit trail saved

Prevention Layer

The first line of defence. Trend’s XGen multi-layer, WatchGuard’s Zero-Trust Application Service, and Kaspersky’s six-layer engine all block threats before execution — stopping known malware, ransomware, zero-days, and fileless attacks at the endpoint perimeter.

Detection Layer

Continuous monitoring of all endpoint behaviour detects anomalies, IoAs, and indicators of compromise that evade prevention. EDR capabilities across all three platforms provide 24/7 visibility into every process, file modification, network connection, and user action.

Response & Remediation Layer

Automated and analyst-guided response actions — process termination, device isolation, file quarantine, ransomware rollback, and policy updates — contain and remediate threats at machine speed before they spread laterally across the organisation.

Threat Intelligence Layer

All three platforms are connected to global threat intelligence networks: Trend’s Smart Protection Network, WatchGuard Collective Intelligence, and Kaspersky Security Network — providing real-time updates on emerging threats as they are discovered worldwide.

iAmaze Managed SOC Layer

iAmaze provides continuous monitoring of your endpoint security environment, daily threat reports, proactive alert triage, policy tuning, and incident response — ensuring your endpoint security posture is always optimised and adapting to the evolving threat landscape.

Cross-Product XDR Correlation

For organisations deploying multiple products, iAmaze integrates endpoint alerts with email, network, and identity security data through XDR correlation — providing a unified view of complex, multi-stage attacks that span multiple security domains.
BUSINESS BENEFITS

Organisations That Should Upgrade Their Endpoint Security Now

Organisations currently relying on basic antivirus solutions without EDR or behavioural detection capabilities

Businesses that have experienced ransomware, malware infections, or fileless attacks and need proven enterprise-grade protection

Companies managing a mix of Windows, macOS, Linux, and mobile devices that need consistent cross-platform security coverage

IT teams without dedicated security analysts who need managed threat hunting and SOC monitoring as part of their endpoint solution

MSPs and multi-site organisations that need centralised, multi-tenant endpoint management with detailed per-client reporting

Regulated industries — BFSI, healthcare, manufacturing, government — requiring compliance-ready endpoint security with full audit trails

WHY iAMAZE

Your Dedicated Endpoint Security Implementation Partner

iAmaze provides end-to-end endpoint security services across all three platforms — from initial assessment and vendor-neutral product recommendation through deployment, policy configuration, user training, and ongoing managed security operations.

EPS Assessment

We audit your current endpoint security posture, identify unprotected devices, analyse gaps in detection coverage, and quantify your risk exposure across platforms and operating systems.

Product Selection

We provide vendor-neutral guidance to match the right product to your organisation: Trend Vision One for XDR breadth, WatchGuard EPDR for Zero-Trust prevention, or Kaspersky Next for deep multi-layer ML protection.

Deployment & Integration

We deploy the chosen solution across all endpoint types — Windows, macOS, Linux, mobile, and servers. We configure policy baselines, exclusion lists, threat intelligence integration, and EDR response rules.

Policy Configuration

We build granular security policies tailored to your organisation’s risk profile: content filtering, application control, device control, network protection, and automated response playbooks.

User Training

We deliver admin training for the security console and end-user awareness sessions ensuring your team understands policies, reporting procedures, and how to respond to endpoint alerts.

24/7 Managed SOC

Ongoing monitoring of endpoint security alerts across your deployed platform. Daily threat intelligence reports, proactive alert triage, incident response, and quarterly security posture reviews with your IT leadership.

HOW WE WORK

Our Four-Step Endpoint Security Engagement

From your first call to full endpoint protection in days — a structured, expert-led approach with minimal disruption to your operations.

EPS Assessment

Audit your current endpoint security posture, identify gaps across platforms, and map which threats are currently undetected or unmitigated.
Product Selection

Recommend the right solution for your environment — Trend Micro for XDR, WatchGuard for Zero-Trust, or Kaspersky for deep ML protection — or a layered combination.
Deployment & Integration

Deploy the chosen endpoint security agent across all devices. Configure policies, exclusions, threat intelligence feeds, and EDR response rules.
Training & Managed SOC

Admin and end-user training. 24/7 monitoring of alerts, threat hunting, incident response, policy tuning, and quarterly security posture reviews.
OUR FEATURE

Protect Every Endpoint in Your Business.

Contact Us

(+91) 981157557

Website

www.iamaze.in

Location

Sector 18, Gurugram, India